


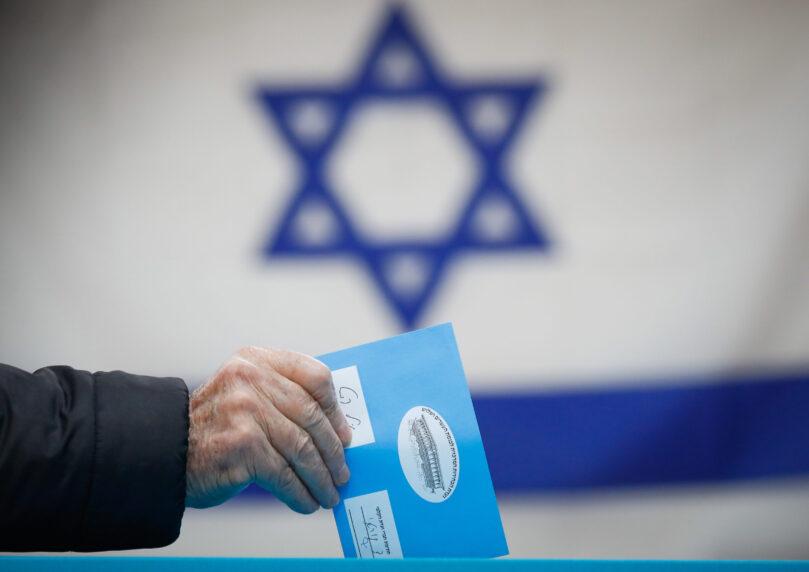
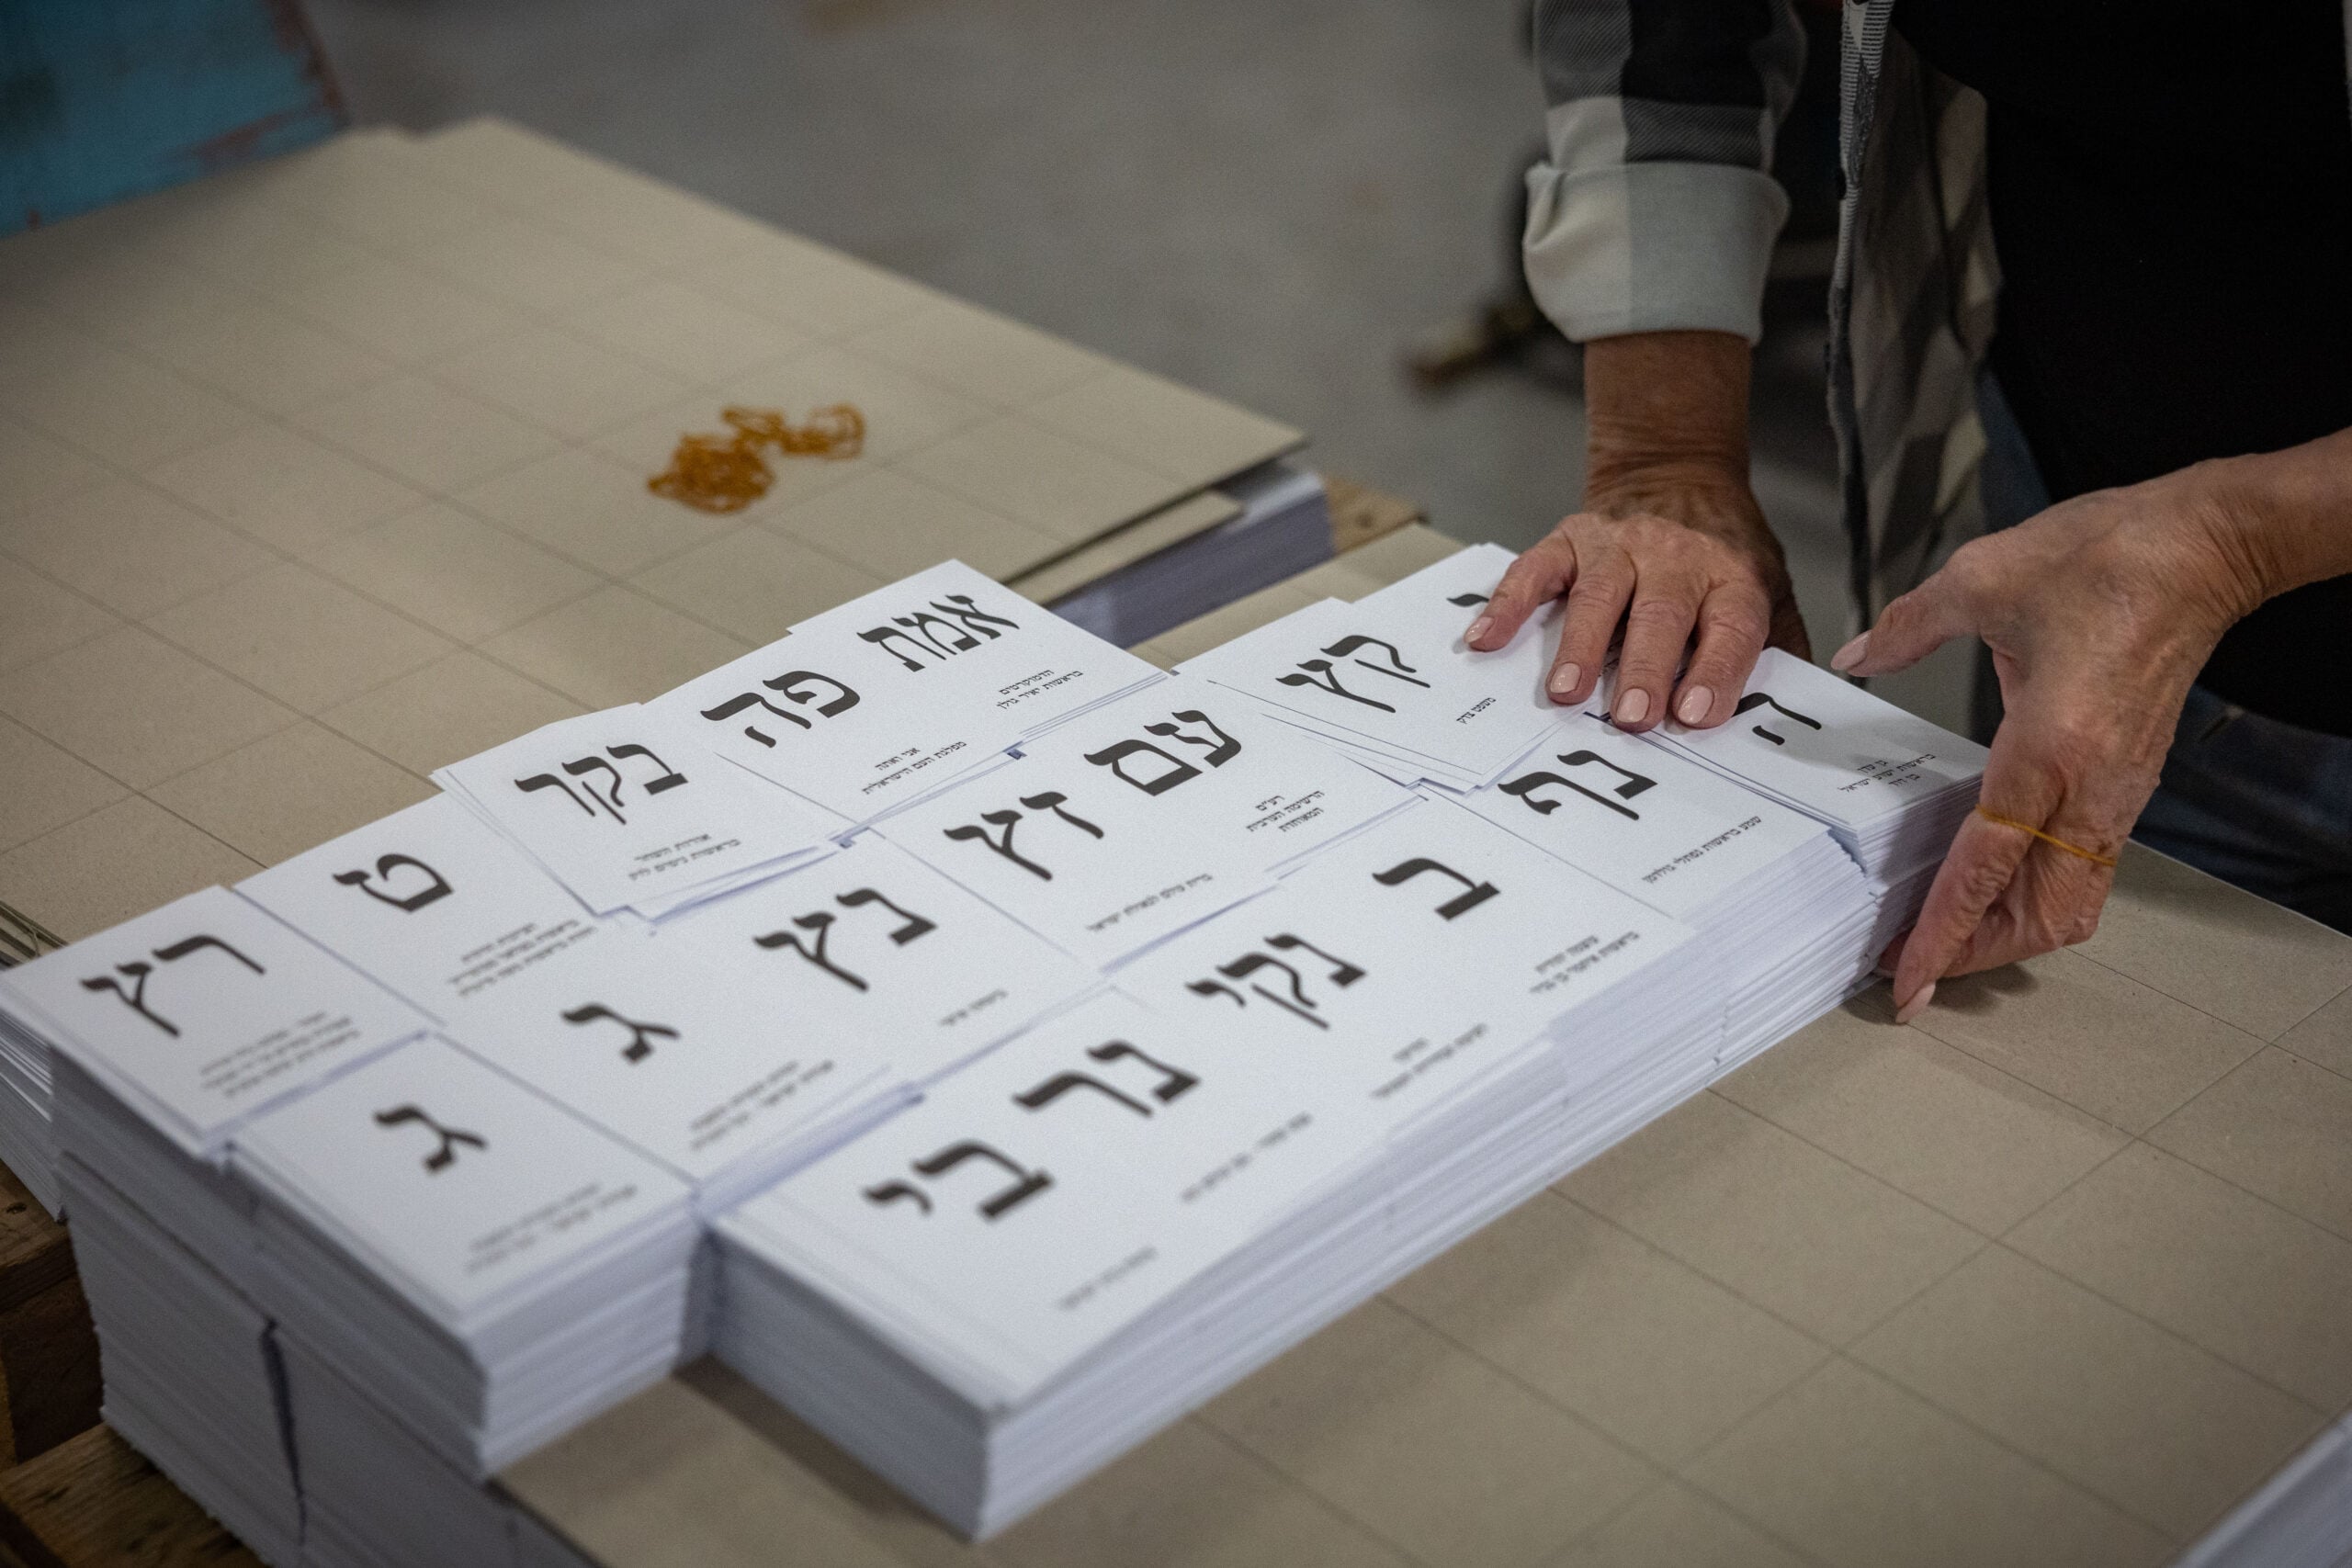
The year 2026 is defined by screens managing nearly every aspect of our lives: we transfer millions of shekels through banks, sign government documents, authenticate ourselves biometrically, and deploy autonomous AI agents. Yet on election day, millions of Israeli citizens are called to put down their phones, walk to a public building, take a printed paper slip, insert it into a sealed envelope, and drop it into a locked blue box. For many, this feels like a frustrating anachronism that raises questions about a technological gap—but for cybersecurity experts and election officials, it’s the greatest strategic strength of Israeli democracy.

 2+
The Difference Between Smartphones and Machines: Two Different Worlds
To understand why the system isn’t going digital, it’s essential to separate two completely different mechanisms that often get confused in public discourse: remote voting via a home app versus computerized voting inside the polling station (EVM). Computerized voting requires physical arrival at a station, and instead of a paper slip the voter presses a touchscreen or swipes a smart card. In contrast, smartphone voting seeks to enable voting from the couch—but opens such a severe threat front that no major Western democracy dares adopt it.
With computerized voting machines at the polling station itself, just a few minutes of physical access—say, during storage, maintenance, or preliminary testing—is enough to plant malware that changes votes, erases logs, and leaves the system looking perfectly normal. With remote voting via smartphone, the threat is even more severe: malware on the voter’s device can display the correct choice on screen but send a different vote to the server, while even a single attacker, from a foreign country or inside the system, can alter or delete hundreds of thousands of votes with the click of a button, without needing complex physical coordination and with no possibility of detection after the fact.
In other words, a built-in mathematical contradiction emerges at the heart of democracy, known as the “election paradox”: the obligation to ensure each person votes only once (strict identity authentication) versus the absolute obligation that no person in the world knows how they voted (complete secrecy). In digital systems, the moment you disconnect the encrypted vote from the voter’s identity to ensure secrecy, it becomes impossible to prove after the fact whether the line of code in the database reflected the voter’s true will, or was corrupted along the way by malware planted on the mobile device.
The Banking Myth: Why What Works for Money Doesn’t Work at the Ballot Box
The most common argument among digital voting advocates rests on the financial comparison: “If my banking app is secure enough to transfer my life savings, why can’t I vote for the Knesset with it?” The answer is simple: the banking system operates in complete opposition to the principle of secrecy. In every financial transaction there’s a transparent documentation chain: the bank knows who sent, who received, at what second, and in what amount. If a hacker breaks into an account and steals money, the system will identify the anomaly, police will track the trail, and the bank will cancel the transaction and return the money. At the ballot box, by contrast, there’s no way to know who was “robbed,” and you can’t return a vote that was changed without exposing the voter’s identity.
This issue leads to the abyssal difference between distributed risk and centralized risk. To forge a hundred thousand paper ballots in the traditional system, a hostile organization would need to recruit, bribe, and coordinate thousands of people simultaneously at thousands of different polling stations across the country—an impossible operation that would be exposed immediately to the eyes of rival party representatives. In contrast, in a nationwide computerized system run from a central server, the risk becomes centralized: a single malicious line of code, a zero-day exploit in the software, or a faulty update from an outside contractor can skew half a million votes in a fraction of a second and in complete silence, without leaving any physical evidence for the human eye.
Europe Tried Too—And Turned Back
Israel’s adherence to paper ballots isn’t unusual in the Western world, but rather aligns with the most stringent countries. Germany and the Netherlands, pioneers in adopting electronic voting machines in the 1990s, canceled their use and returned to paper. In 2009, Germany’s Federal Constitutional Court ruled that voting machines were unconstitutional, establishing the “principle of publicity”: every ordinary citizen, without training in software engineering or knowledge of cryptography, must be able to understand, see, and personally oversee how votes are recorded and counted. The Dutch returned to the ballot and red pencil after studies proved it was impossible to guarantee voting secrecy against electronic eavesdropping.
 2+
The only country that has adopted full online voting is Estonia, where over half of citizens vote via the internet. However, international security experts from leading U.S. universities continue to publish reports pointing to structural weaknesses in the Estonian system, emphasizing that it relies on a unique digital ID infrastructure that doesn’t exist in other countries. Moreover, Estonia’s voting data over two decades shatters a central myth: internet voting barely raises overall turnout (a net addition of less than a single percentage point), but merely provides convenience to citizens who would have bothered to get to the polls anyway.
AI Force Multipliers and Public Trust
In the current era, the artificial intelligence revolution intensifies risk gaps. AI models and autonomous agents don’t invent new threats, but they reduce the barrier to entry for sophisticated breaches to zero, scan code repositories in seconds, and locate system vulnerabilities at superhuman speed. In a country like Israel, under constant cyberattacks from Iran and its proxies, deploying a computerized election system would turn election day into a top-tier strategic attack target that could paralyze the state.
The fact that voting itself is conducted on paper allows security agencies and the national cyber apparatus to concentrate efforts on defending the information space around the elections. Instead of dealing with a breach of ballot boxes, the effort focuses on blocking deepfake videos, synthetic voice recordings of politicians, bot networks, and data poisoning designed to mislead the public before they enter the voting booth. The physical ballot ensures that even if the network is flooded with disinformation, the democratic mechanism itself remains completely immune to signal disruption.
Former director general of the Central Elections Committee Orly Ades defined this approach in an interview with Calcalist as “institutional resilience”: paper ballots aren’t evidence of backwardness, but an insurance policy with no substitute. At every polling station in Israel sit representatives of rival parties who check each other, count every envelope twice, and sign a physical protocol together. Paper is tangible material that doesn’t depend on the electrical grid or servers, and can be opened, examined, challenged, and recounted by the human eye under a judge’s supervision.
 2+
Ultimately, the most important value in elections isn’t the speed of producing results, but public trust in their integrity. Walking to the polling station, spreading out the ballots behind a cardboard partition, and dropping the envelope into the box may seem outdated in the autonomous era of 2026, but this simplicity is precisely the tool still considered safest against blind algorithms, ransomware attacks, and foreign powers determining who will lead the State of Israel.